

Governance
Deciding what an agent may reach: roles, restrictions, frozen arguments, the audit trail afterwards, and what happens when somebody leaves.
Scheduled AI agent tasks, governed in advance
Scheduled AI agent tasks run with nobody present to approve, so the controls that count are set first: role restrictions, frozen arguments, a narrowed grant.
 Uday Gajavalli
EU data residency for AI agents, leg by leg
EU data residency for AI agents spans three legs: the app, the control plane and the model. Elaichi's eu region pins the data store and tool calls to the EU.
 Nachi Raman
Human approval for AI agent actions: the layers
Human approval for AI agent actions comes in layers: a prompt for the person asking, then the role rules, frozen values and requests an admin decides.
 Roopendra Talekar
MCP security review checklist: ten questions
An MCP security review checklist: ten questions to ask before approving an MCP server or gateway, what a good answer looks like, and Elaichi's answers.
Uday Gajavalli
MCP security risks and how to reduce them
The MCP security risks a company faces, from prompt injection to keys in local configs, with an example and a fix for each, and who owns the fix.
Uday Gajavalli
How to roll out Claude and ChatGPT to employees
Roll out Claude and ChatGPT to employees in order: approve apps, connect them once, build team toolboxes, map roles, pilot, onboard and offboard.
Uday Gajavalli
Audit Log Retention: AI Actions at 90 Days vs Seven Years
Elaichi keeps 90 days of audit log retention, AI actions included. A seven-year mandate needs a customer-owned destination, and only Datadog delivers today.
Connect Vanta to Claude for compliance work
To connect Vanta to Claude for compliance work, add it as one connector, allow only its read tools, and prove the limit from the audit log.
Uday Gajavalli
The Allow Rule That Blocks All Tools
The allow rule that blocks all tools is the one that names nothing: it turns on the allowlist for its target and blocks every connector and tool.
Uday Gajavalli
Least privilege for AI agents without breakage
Least privilege for AI agents starts from what your pilot actually called: narrow to that recorded set, then confirm the rule landed before you trust it.
 Raajshekhar Rajan
SOC 2 evidence for AI agents: CC6 and CC7
SOC 2 evidence for AI agents maps to CC6.1, CC6.2, CC6.3 and CC7.2: who can reach what, how access starts and ends, and a log of each executed tool call.
Roopendra Talekar
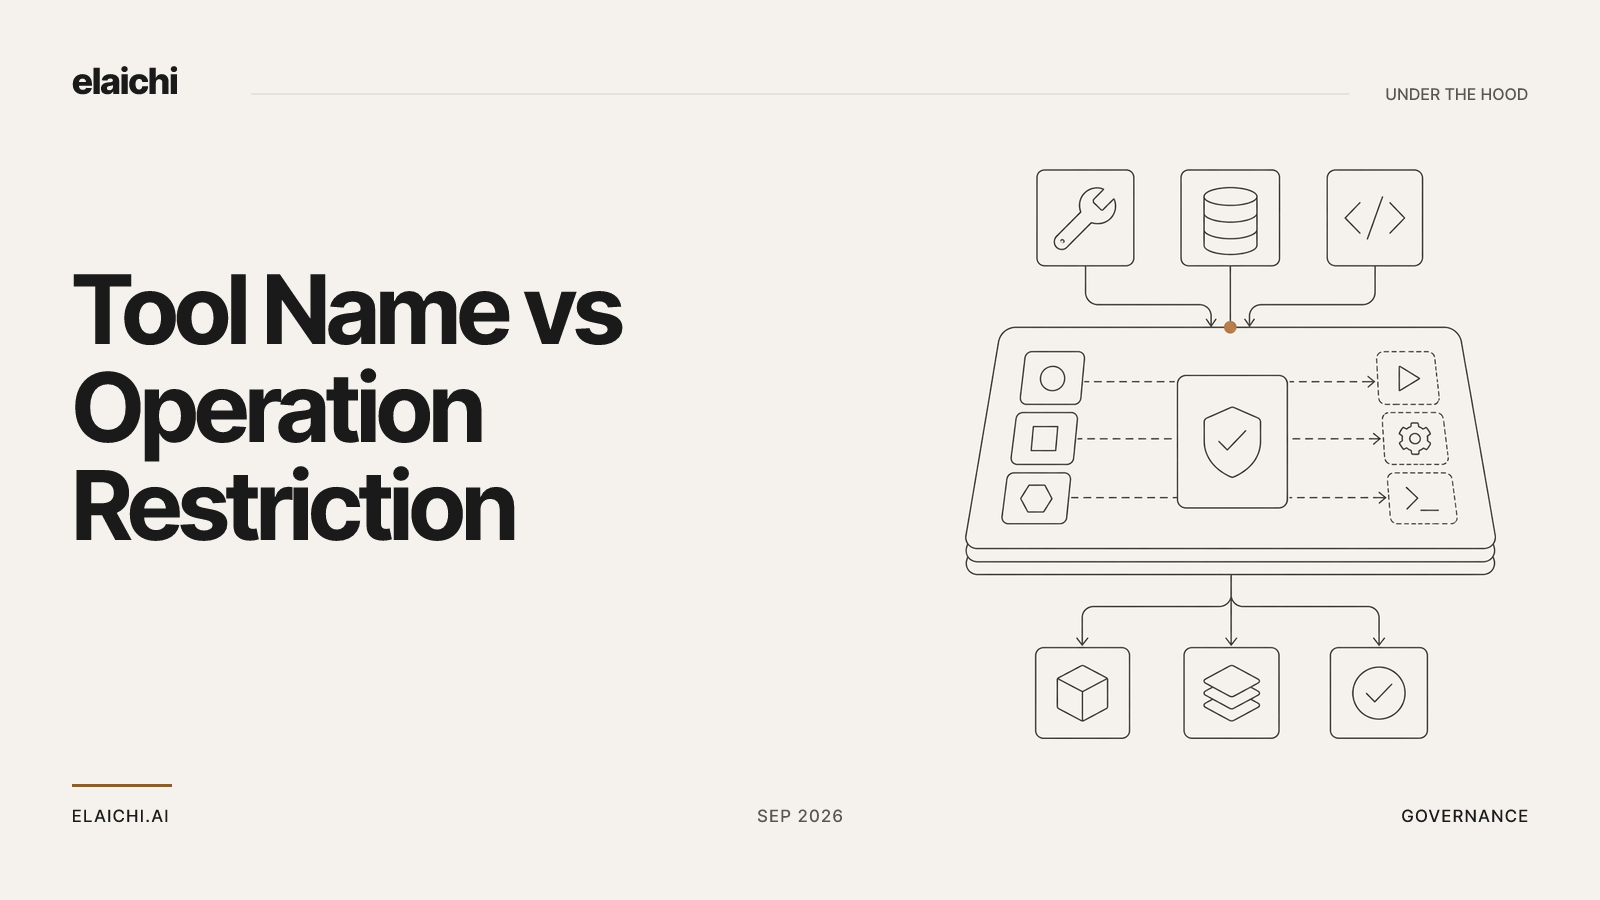
Why blocks match tool names but allows don't
In Elaichi, blocks match tool names or the operation behind them, while allows match the operation only, so a renamed tool can never widen a role's reach.
Uday Gajavalli
Lock AI agent tool arguments, like a wire's payee
Lock AI agent tool arguments with frozen parameters: Elaichi removes the field from the model's schema and writes your value over whatever the call sends.
Uday Gajavalli
Designing roles for AI agents: one role each
Design roles for AI agents as one complete job per person: Elaichi gives each member exactly one role and leaves which tools they reach to restrictions.
Raajshekhar Rajan
AI agents and PHI: four questions for your BAA
AI agents and PHI raise four BAA questions, all about access: minimum necessary, audit controls, workforce clearance and what happens when someone leaves.
Roopendra Talekar
What an AI agent audit log must capture
An AI agent audit log must capture who acted, which client called, which account was reached, what was tried and how it ended. Argument contents stay out.
Nachi Raman
Is Composio secure enough for enterprise use?
The answer to "is Composio secure enough for enterprise use" sits in architecture more than controls: its own pages list SSO, role permissions and call logs.
Nachi Raman
Restrict one AI tool or the whole app? Six cases
Restrict one AI tool when a role needs part of an app, and block the whole app when it needs none of it. Six cases, and what new tools do to each rule.
Roopendra Talekar
Offboarding AI access, contractors included
Offboarding AI access in Elaichi takes effect on the next call. Here is what the removal preflight checks, and the order that works.
Nachi Raman
Put AI to work in your own apps
14 days of Black, no credit card. Start with one app and one team.
When the trial ends, nothing is deleted. You move to the free Personal plan, and connections, roles and the audit log stay where they are.
 Add one link to your AI app
The same link for everyone on your team.
https://api.elaichi.ai/mcp
 ChatGPT
 Claude
 Cursor
 Microsoft Copilot